
Inside North Korea’s Ruthless Hacking Operations: The $6.3B Binance Heist Suspects
Discover how North Korean state-sponsored hackers—prime suspects in the $6.3B Binance heist—target people, not code, to pull off devastating cybercrimes.
Page views: 2
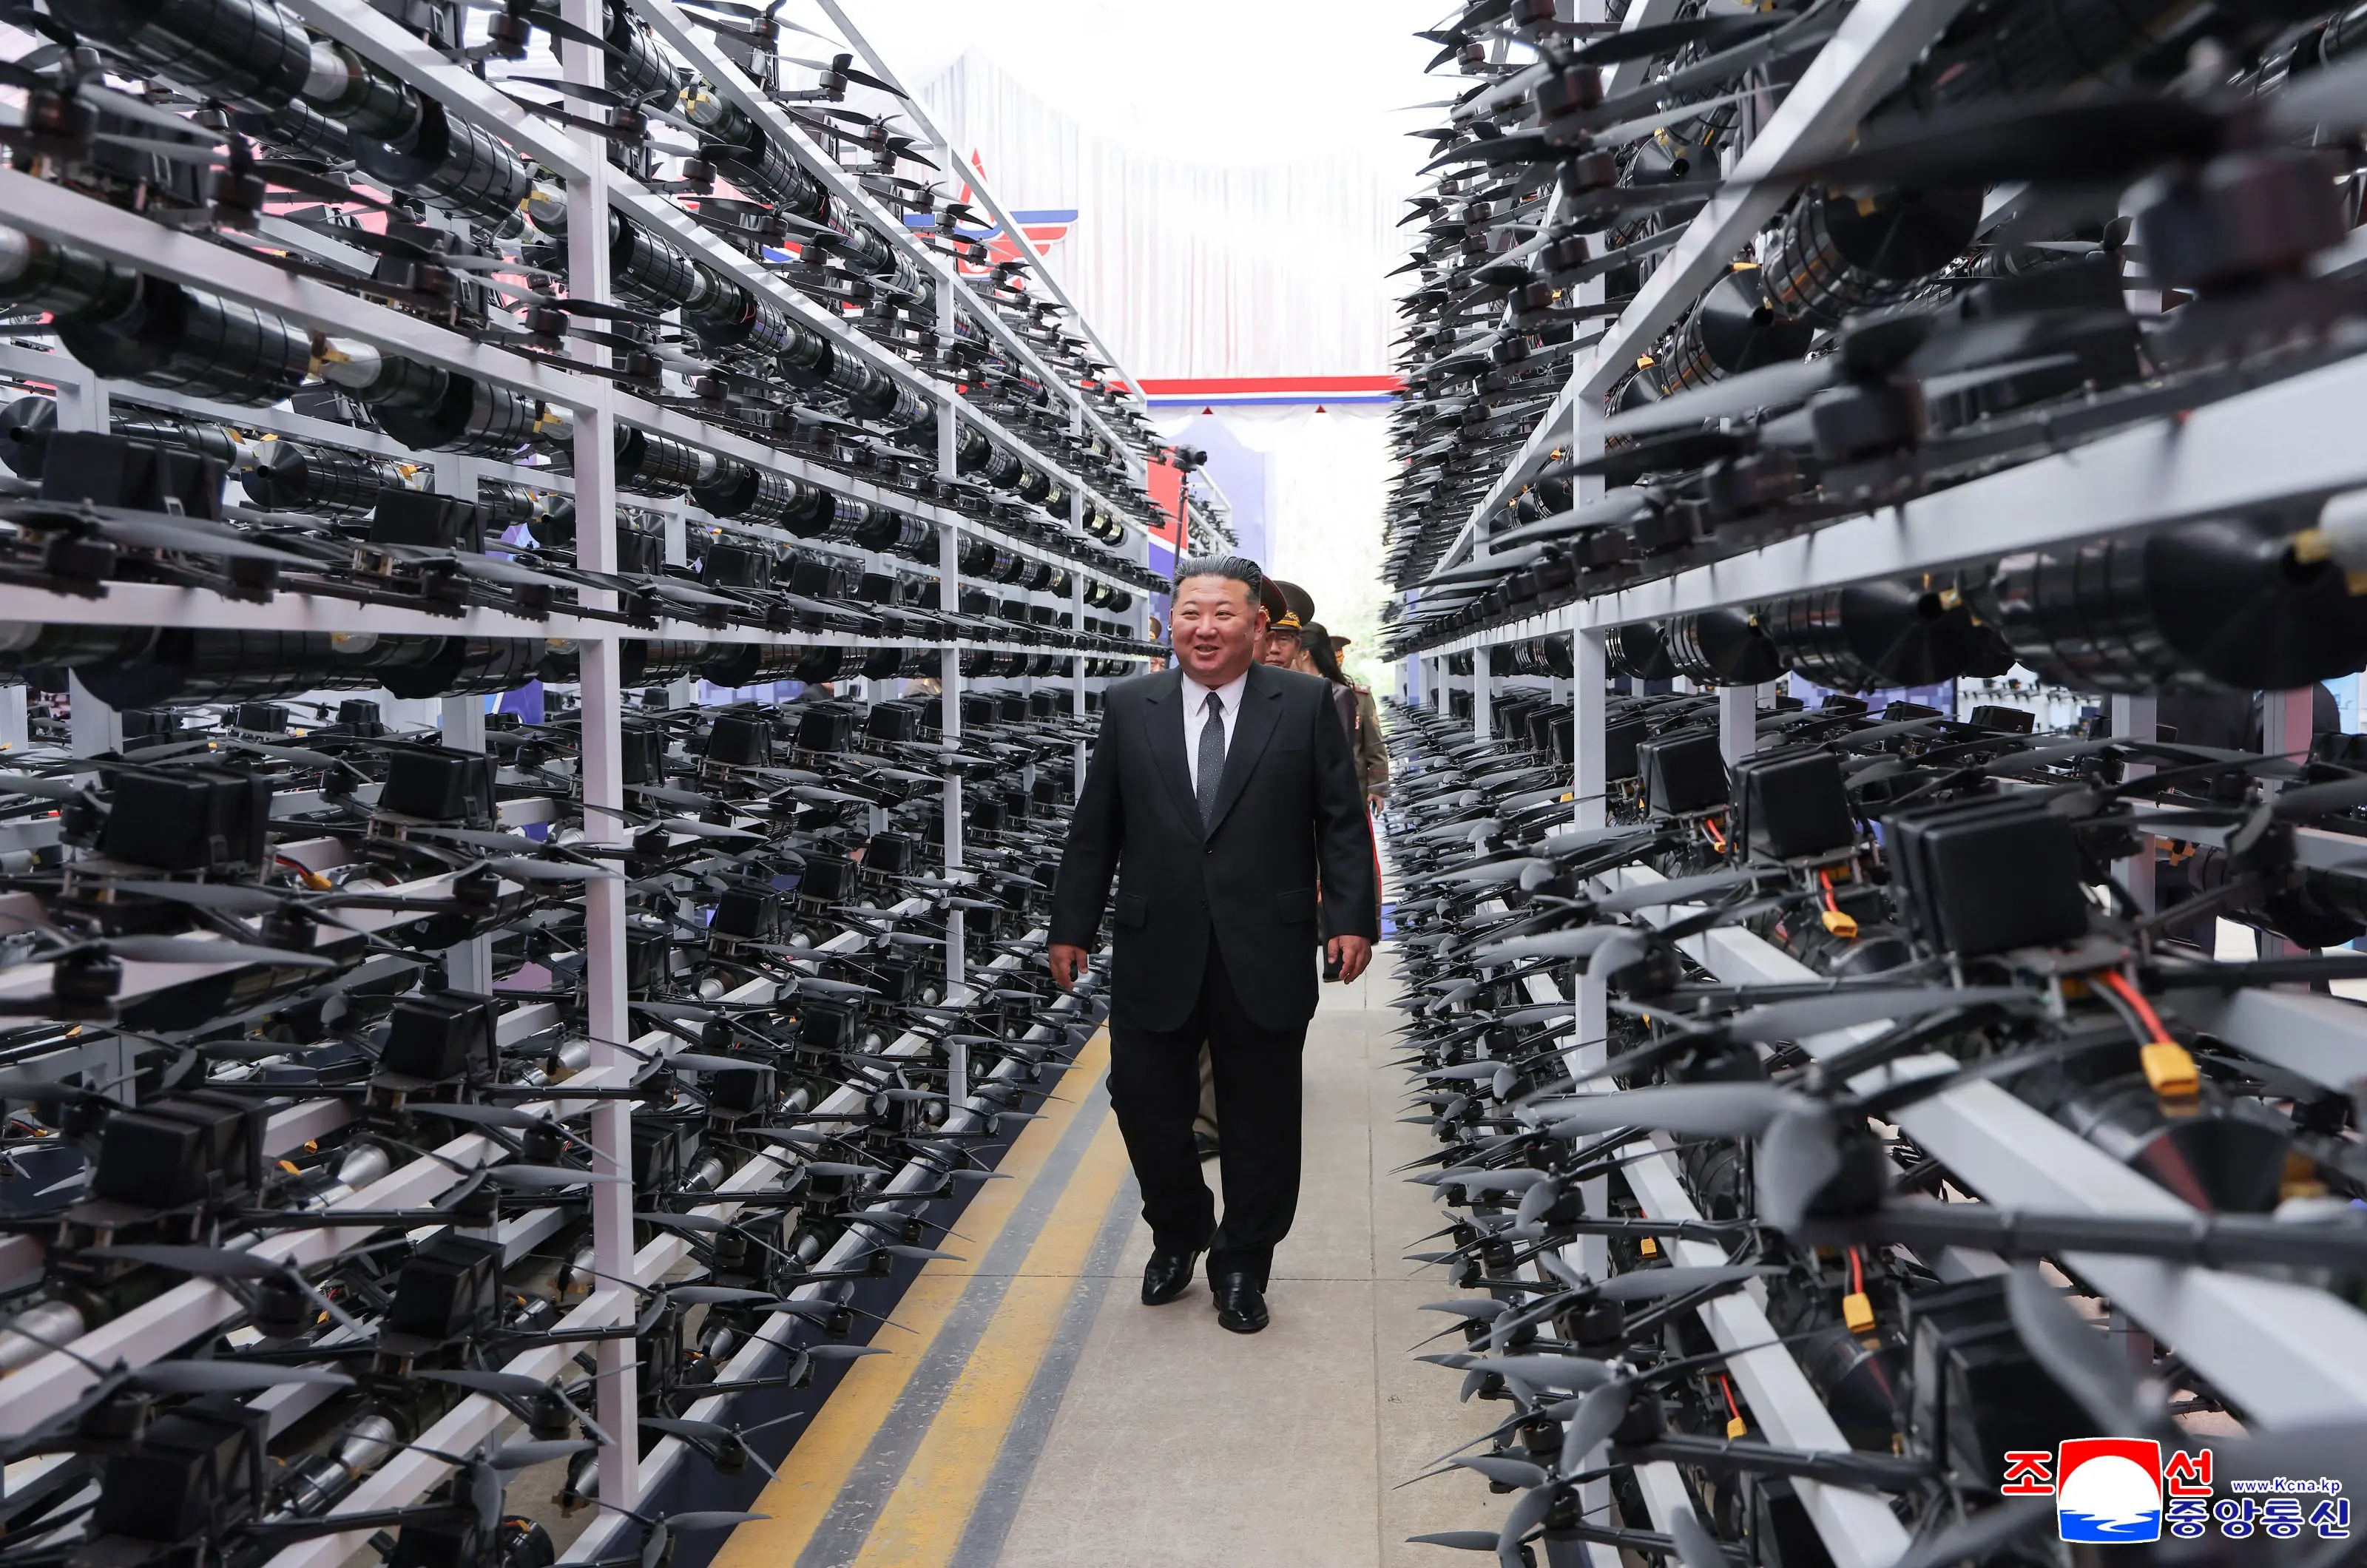
North Korea’s state-sponsored hackers are not average cybercriminals. They are disciplined, ruthless, and singularly focused on funding the regime. When news broke of the massive $6.3B Binance heist, all eyes turned to Pyongyang’s elite digital units. But what truly sets them apart? As one cybersecurity expert told The Post: "They attack people, not code."
The Human Entry Point
Instead of searching for obscure software flaws, these hackers launch carefully crafted phishing campaigns, impersonate trusted vendors, and even target employees’ personal devices. By studying victims’ habits, languages, and relationships, they gain access to systems that no firewall can protect. At the heart of their operations is social engineering: they don’t rely solely on malware—they rely on human error.
The $6.3B Binance Heist: A Case Study
A single click on a malicious link by an exchange employee can expose private keys, wallet credentials, and internal dashboards. In the Binance heist, suspected North Korean operators allegedly used a combination of fake job offers, poisoned software packages, and privilege escalation to bypass security. Once inside, they moved laterally, disabled alerts, and began moving assets. Experts believe they laundered funds through chain-hopping, decentralized bridges, and mixers to obscure the trail—leaving investigators with a daunting puzzle.
Why “Attack People, Not Code” Matters
Understanding this mindset is critical. Firewalls and encryption are useless if an attacker can trick someone into opening the castle gate. North Korean hackers monitor job postings, chat in Telegram groups, and attend crypto conferences—all to map their targets. They exploit ambition, curiosity, and trust. For defenders, this means security must be a human discipline: regular training, multi-factor authentication, and strict verification processes are just as important as advanced software.
Staying Ahead of the Threat
Cryptocurrency exchanges have responded with stronger KYC, withdrawal limits, and AI-based anomaly detection. But the threat remains. As long as digital assets are valuable and pseudonymous, North Korea’s ruthless state-sponsored hackers will keep attacking the human element. The best defense? Treat every message, link, and request as a potential attack—because when it comes to these hackers, the target is always people.
Published on: October 31, 2026, 8:03 am