
Bloom Solana Trading Bot Exploit: $947K Drained, Reimbursements Promised
A Telegram trading bot lost $947K in SOL from 9 users. Bloom blames a third-party flaw, promises full reimbursement, but critical questions remain unanswered.
Page views: 2
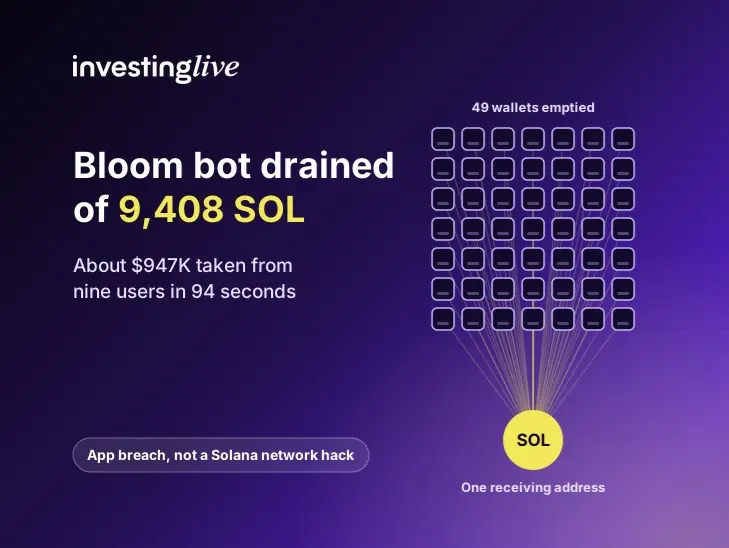
On October 26, Bloom, a popular Solana trading bot on Telegram, suffered a security breach that drained about 9,408 SOL — worth roughly $947,000 — from 49 wallets belonging to nine users. On-chain monitoring service Onchain Lens flagged the outflows to a single receiving address at 04:26 UTC. Early blockchain estimates put the loss slightly higher, at about $954,000. Bloom has promised to reimburse every affected user in full and has paused some services while it investigates.
What Happened?
Bloom attributes the attack to a remote code execution vulnerability in a third-party module. The company says no private keys were compromised and unaffected wallets are safe. However, blockchain data firm Bitquery found that every transfer was validly signed by the source wallet's own key, and the full sequence across 48 wallets took just 94 seconds. Bitquery could not establish how the attacker obtained that signing authority. Some drained wallets had been inactive for months, and the order of the withdrawals suggests the targets were organized before the attack began.
Why It Matters for Solana and Telegram Bots
The theft is too small to move SOL on its own, but it lands on a fragile tape. SOL has fallen about 14% in October, the weakest of the four largest cryptocurrencies, as spot Solana ETF outflows and a broad pullback from crypto risk weigh on sentiment. The more lasting effect may be on the Telegram trading bot segment, where users give up some control of signing in exchange for speed. If confidence in that model weakens, memecoin and short-term trading activity could ease — and much of that activity runs on Solana.
What Users Should Do
Bloom advises users to move remaining funds to new wallets with freshly generated keys. This incident is a breach of one application, not the Solana network itself, but it shows the trade-off behind bot convenience. A weakness anywhere in the software can put funds at risk, even when the underlying blockchain works as designed.
What to Watch Next
The next key development is Bloom's root-cause report. It must explain how validly signed transfers were possible without private key exposure. Confirmation that reimbursements have reached all nine users would ease concern. Evidence of wider key exposure would turn a contained incident into a broader question about bot security. Any movement of funds from the receiving address is also worth monitoring. The loss is small next to April's $285 million Drift Protocol exploit, but for the Telegram bot niche, this episode may be a turning point.
Published on: October 27, 2026, 8:03 am